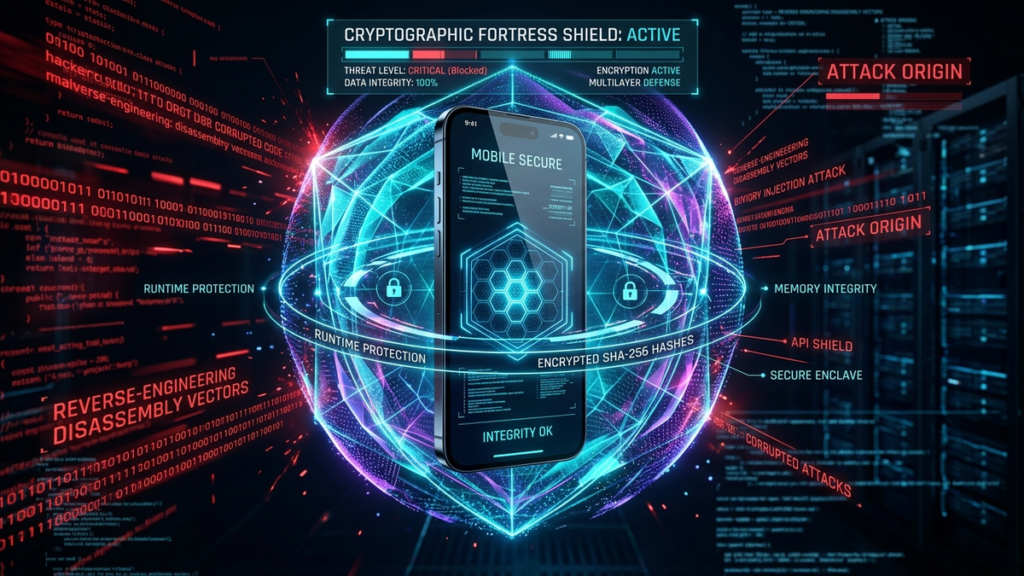
Every compiled mobile application published to the Google Play Store or Apple App Store is an untrusted binary running in a hostile environment. Unlike backend cloud servers protected behind enterprise firewalls, client-side mobile applications can be freely downloaded, decompiled, modified, and instrumented by malicious actors. In financial technology, enterprise communications, and gaming applications, failure to harden the client binary leads to catastrophic API abuse, intellectual property theft, and financial fraud.
In 2026, basic source minification is wholly inadequate against automated reverse-engineering suites. At Ghayma LLC, our mobile security practice implements defense-in-depth security architectures that protect client applications against runtime code injection, memory inspection, and binary modification.
1. The Threat Vector: How Attackers Deconstruct Mobile Apps
Modern reverse engineers employ automated, highly sophisticated toolchains:
- Static Decompilation (JADX, Ghidra, IDA Pro): Converting DEX bytecode or ARM64 assembly back into readable source code, exposing proprietary business logic, hardcoded secrets, and unauthenticated API routes.
- Dynamic Runtime Hooking (Frida, Xposed): Injecting shared libraries directly into the running application process to intercept function calls, bypass biometric authentication checks, and tamper with SSL certificate pinning logic.
- Compromised Host Environments (Magisk, RootHide, Dopamine): Gaining kernel-level root access to read protected app sandboxes, dump SQLite keychains, and modify device hardware identifiers.
2. Hardware-Backed Device Attestation: The Modern Gold Standard
Historically, mobile developers wrote client-side checks for the /system/bin/su binary or Cydia directories. Attackers trivialized these with one-click Frida hook scripts that returned false to any root check function. In 2026, client-side checks are obsolete.
Production security relies on Cryptographic Remote Attestation backed by hardware secure enclaves:
Play Integrity API (Android) & DeviceCheck / App Attest (iOS)
Rather than relying on client verification, the mobile operating system’s Trusted Execution Environment (TEE / Secure Enclave) generates a cryptographic challenge signed by Apple or Google root certificate authorities. The mobile client sends this attestation token to your backend server, which validates:
- The binary has not been modified or re-signed (Binary Integrity).
- The operating system kernel has not been compromised (Device Integrity).
- The app was genuinely acquired from the official store (Licensing Integrity).
3. Binary Obfuscation and Control Flow Flattening
Standard ProGuard or R8 simply renames variables from verifyCreditCardNumber() to a(). The structural control flow, loops, and logic branches remain completely intact. Advanced enterprise obfuscation (such as DexGuard or LLVM-based OLLVM) alters the fundamental execution graph:
Control Flow Flattening Explained
The compiler breaks every nested if-statement and loop into isolated basic blocks. These blocks are embedded inside a centralized infinite switch-statement driven by a dynamic state variable. To a reverse engineer inspecting the disassembly, the function appears as a chaotic, impenetrable state machine maze that defeats automated decompiler analysis.
4. Defending Against Frida and Dynamic Memory Tampering
To prevent dynamic runtime hooking, production mobile binaries deploy proactive anti-debugging watchdogs:
// Low-level POSIX ptrace anti-debugging check in native C/C++
#include <sys/ptrace.h>
#include <unistd.h>

void enforce_anti_debugging() {
    if (ptrace(PTRACE_TRACEME, 0, 1, 0) < 0) {
        // Debugger or Frida agent already attached!
        // Immediately scrub sensitive encryption keys from memory and terminate
        explicit_bzero(active_session_token, sizeof(active_session_token));
        _exit(1);
    }
}
Furthermore, native background threads monitor memory for known Frida injection signatures (such as open named pipes, default port 27042, and mapped memory pages matching frida-gadget.so), triggering deterministic session invalidation upon detection.
5. Secure Cryptographic Storage & Certificate Pinning
Enterprise applications must enforce zero trust in local storage:
| Security Layer | Vulnerable Practice | Hardened Enterprise Standard |
|---|---|---|
| Data at Rest | Raw SharedPreferences / UserDefaults | EncryptedSharedPreferences (Android Keystore) / Keychain Services (iOS Secure Enclave) |
| Transport Layer | Default OS Trust Store | Public Key Pinning (HPKP) with backup rotation pins and Certificate Transparency monitoring |
| API Secrets | Hardcoded API keys in strings.xml | Short-lived HMAC tokens minted dynamically via backend OAuth token exchange |
“Security is not a binary state; it is an economic barrier. Your objective as an engineer is to raise the computational and time cost of reverse-engineering your binary so high that an attacker abandons the effort.”
Conclusion
Protecting modern mobile applications demands an aggressive, defense-in-depth posture. By combining hardware-backed attestation (App Attest and Play Integrity), native control flow flattening, proactive anti-debugging routines, and strict cryptographic key isolation, mobile engineering teams can safeguard their users, protect corporate intellectual property, and preserve platform integrity.